Mihir Shah
CompTIA Security+ Certified Cybersecurity Analyst with hands-on experience in SOC operations, SIEM management (Splunk, Wazuh), and incident response. Proven ability to design automated threat detection workflows using Python and n8n to reduce alert fatigue. Experienced in vulnerability remediation, PII encryption, and ensuring regulatory compliance with HIPAA and GDPR.
About
A bit about me
Hello! I'm Mihir Shah, a passionate cybersecurity professional dedicated to safeguarding digital systems from evolving threats. My journey in cybersecurity began during my B.Tech studies at Navrachana University, where I developed a strong foundation in programming, networking, and security principles.
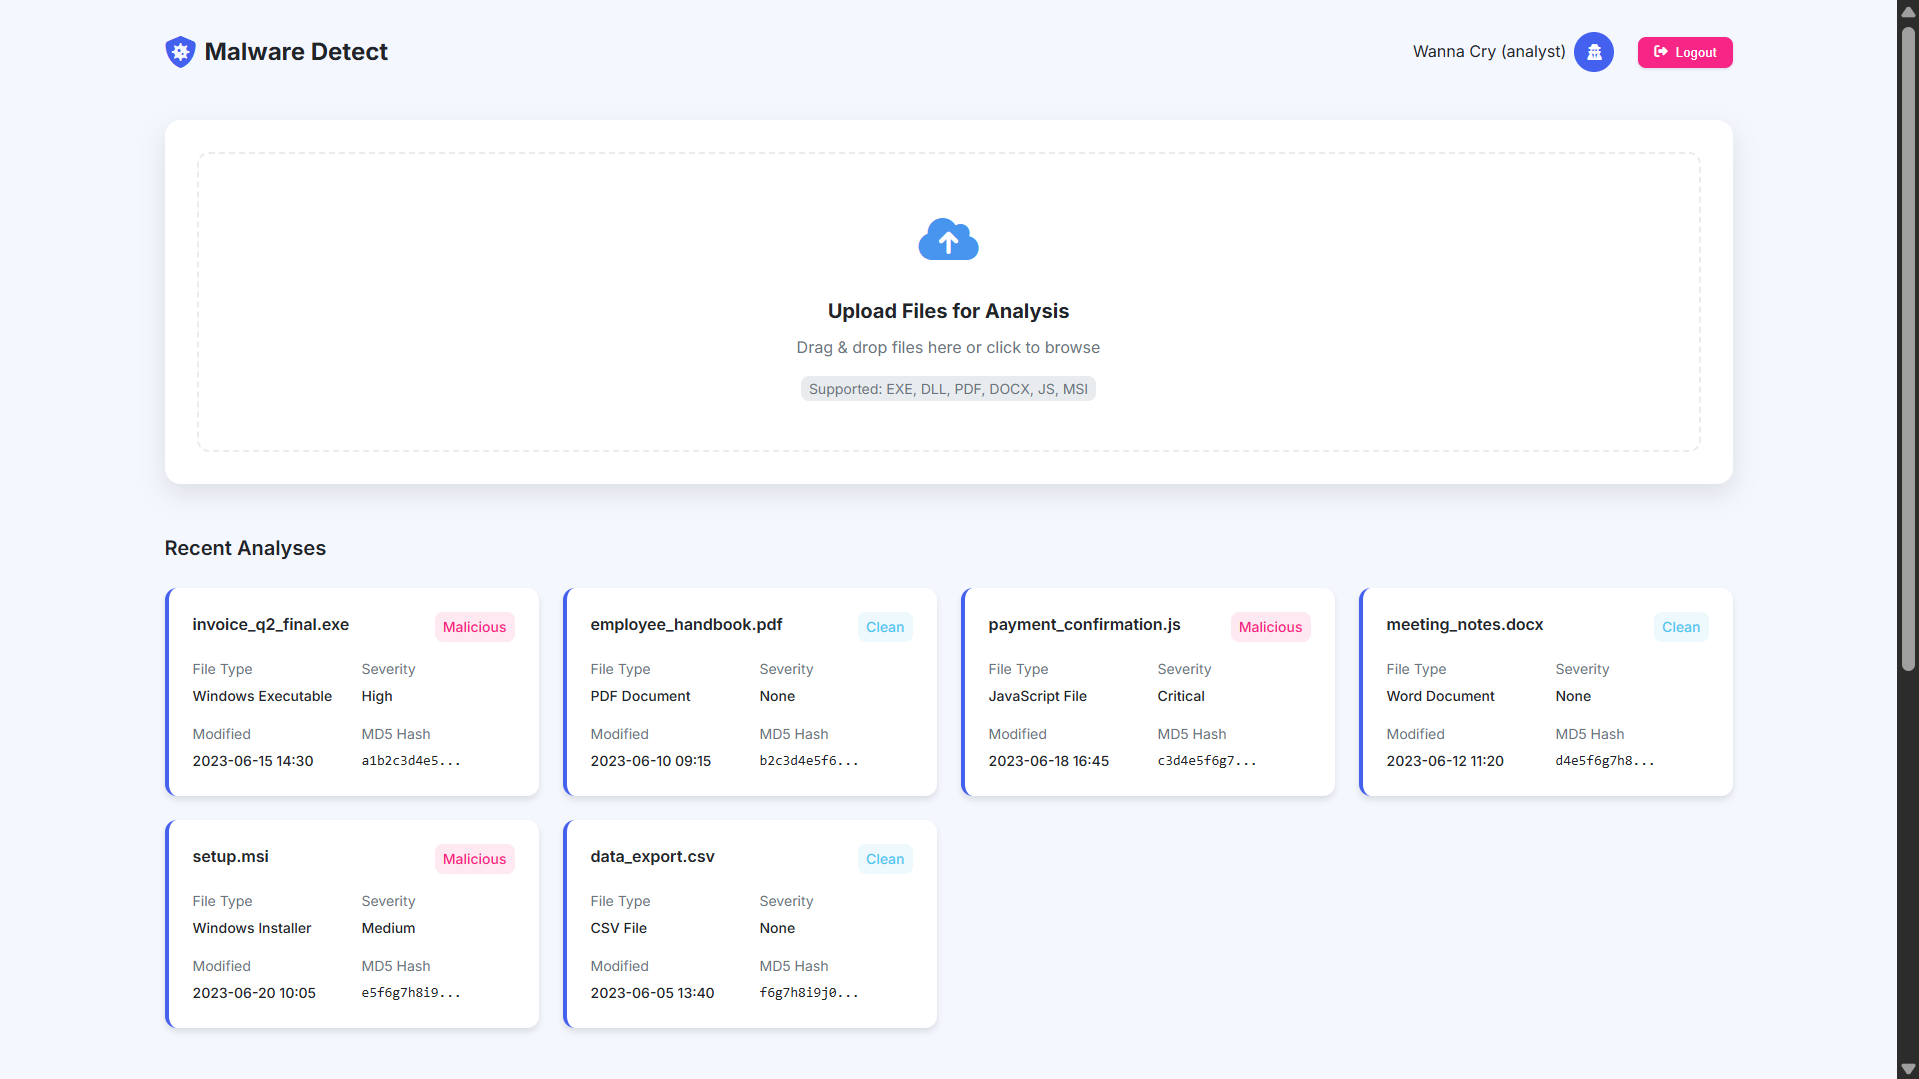
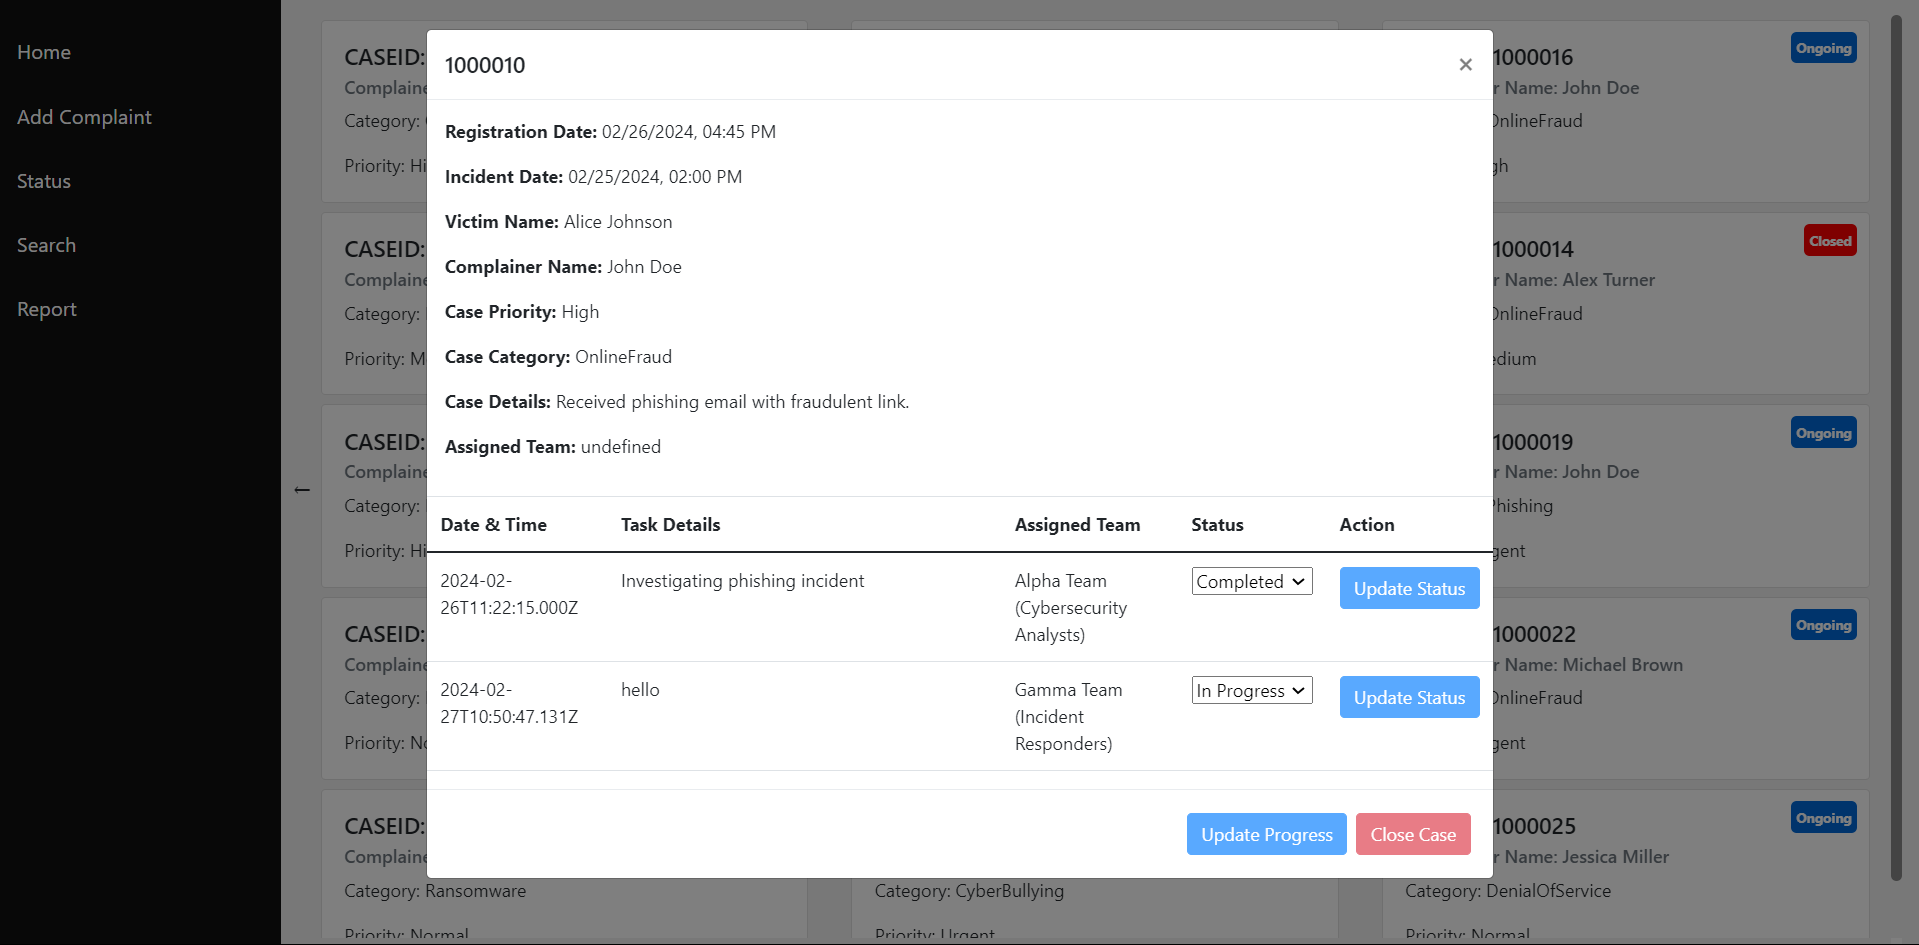
During my internship at Heuristic Pharma Perceptions, I contributed to building secure backend infrastructure for a pre-launch landing page, honing my skills in secure development and teamwork. My projects, such as a malware detection tool using Yara rules and CNN classification, and a Cyber Crime Reporting Portal for law enforcement, reflect my commitment to creating practical, impactful cybersecurity solutions.
My approach to cybersecurity is proactive and multifaceted—I believe in combining automation, threat intelligence, and robust frameworks like the Cyber Kill Chain to build resilient defenses. I'm constantly learning, with certifications like Google Cybersecurity and AWS Academy Cloud Security Foundations, to stay ahead of emerging threats and technologies.
Expertise
Skills & Capabilities
Ethical Hacking
Conducting authorized simulated cyberattacks on computer systems to identify and fix security vulnerabilities before malicious actors can exploit them.
Network Security
Implementing policies and controls to protect network infrastructure, including firewalls, IDS/IPS, VPNs, and secure network architecture design.
Encryption
Expertise in cryptographic protocols, key management, and implementing encryption solutions to protect sensitive data both at rest and in transit.
Secure Coding
Application security testing, code reviews, and implementing secure coding practices to prevent common vulnerabilities like XSS, CSRF, and SQL injection.
Malware Analysis
Analyzing malicious software to understand its behavior, indicators of compromise (IOCs), and techniques used, aiding in threat intelligence and response.
Windows Log Analysis
Monitoring and interpreting Windows Event Logs to detect suspicious activity, investigate incidents, and support digital forensics and SOC operations.
Portfolio
Featured Projects
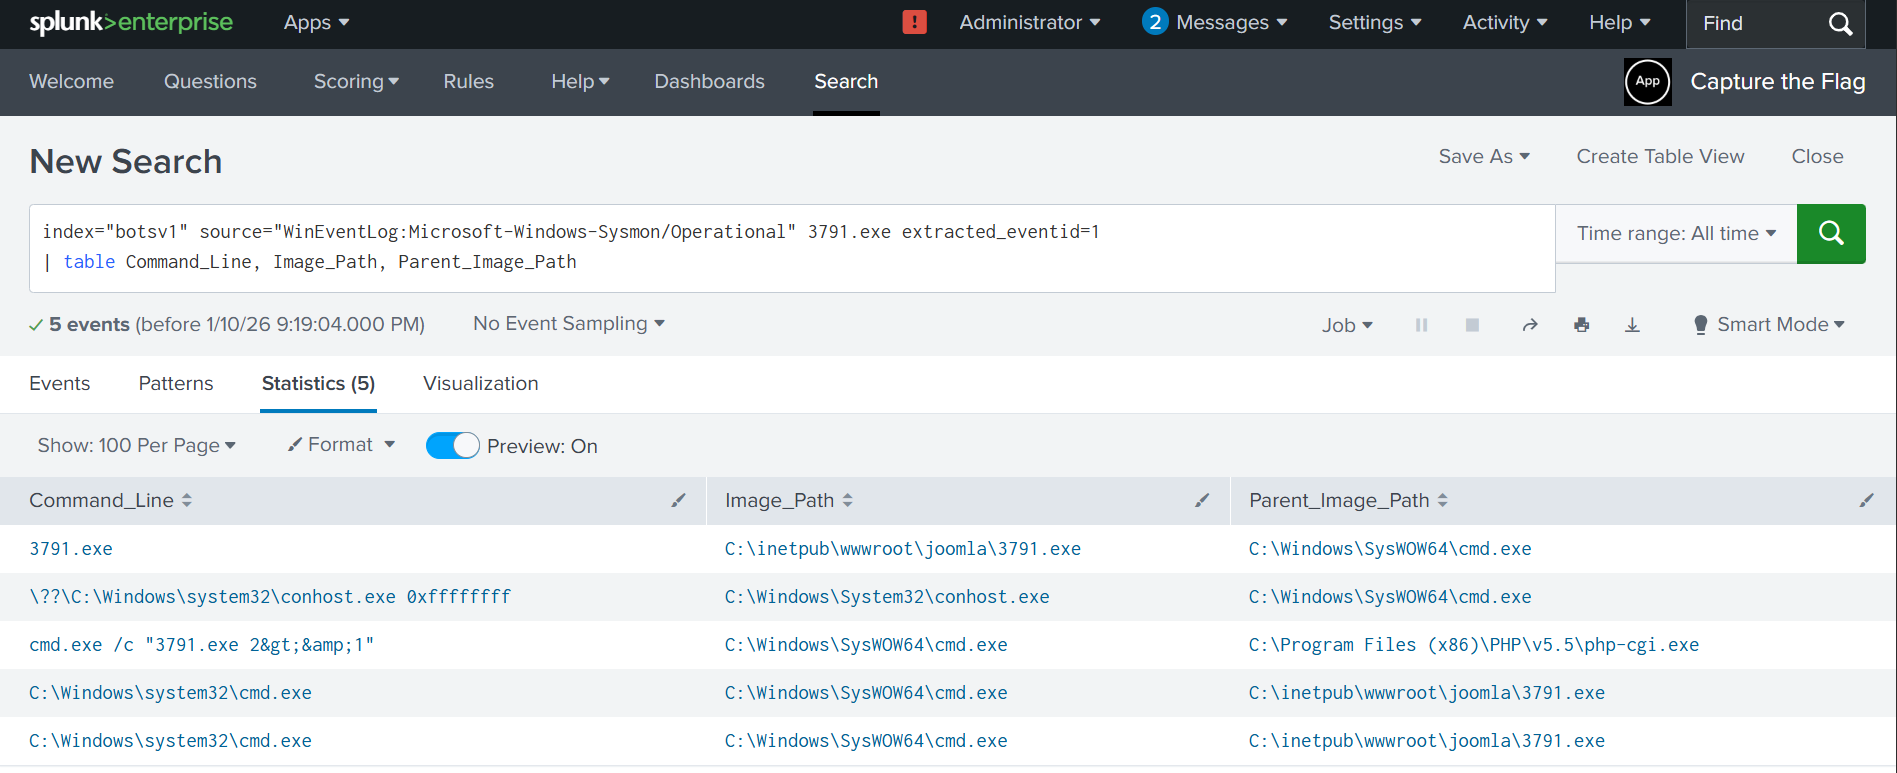
Splunk BOTSv1: Incident Investigation
Led a comprehensive forensic investigation into a multi-stage APT simulation. Analyzed 1M+ logs to reconstruct an attack timeline from initial web-server brute force to lateral movement and data exfiltration demonstrating the ability to distinguish between noise and critical risk in high-pressure scenarios.
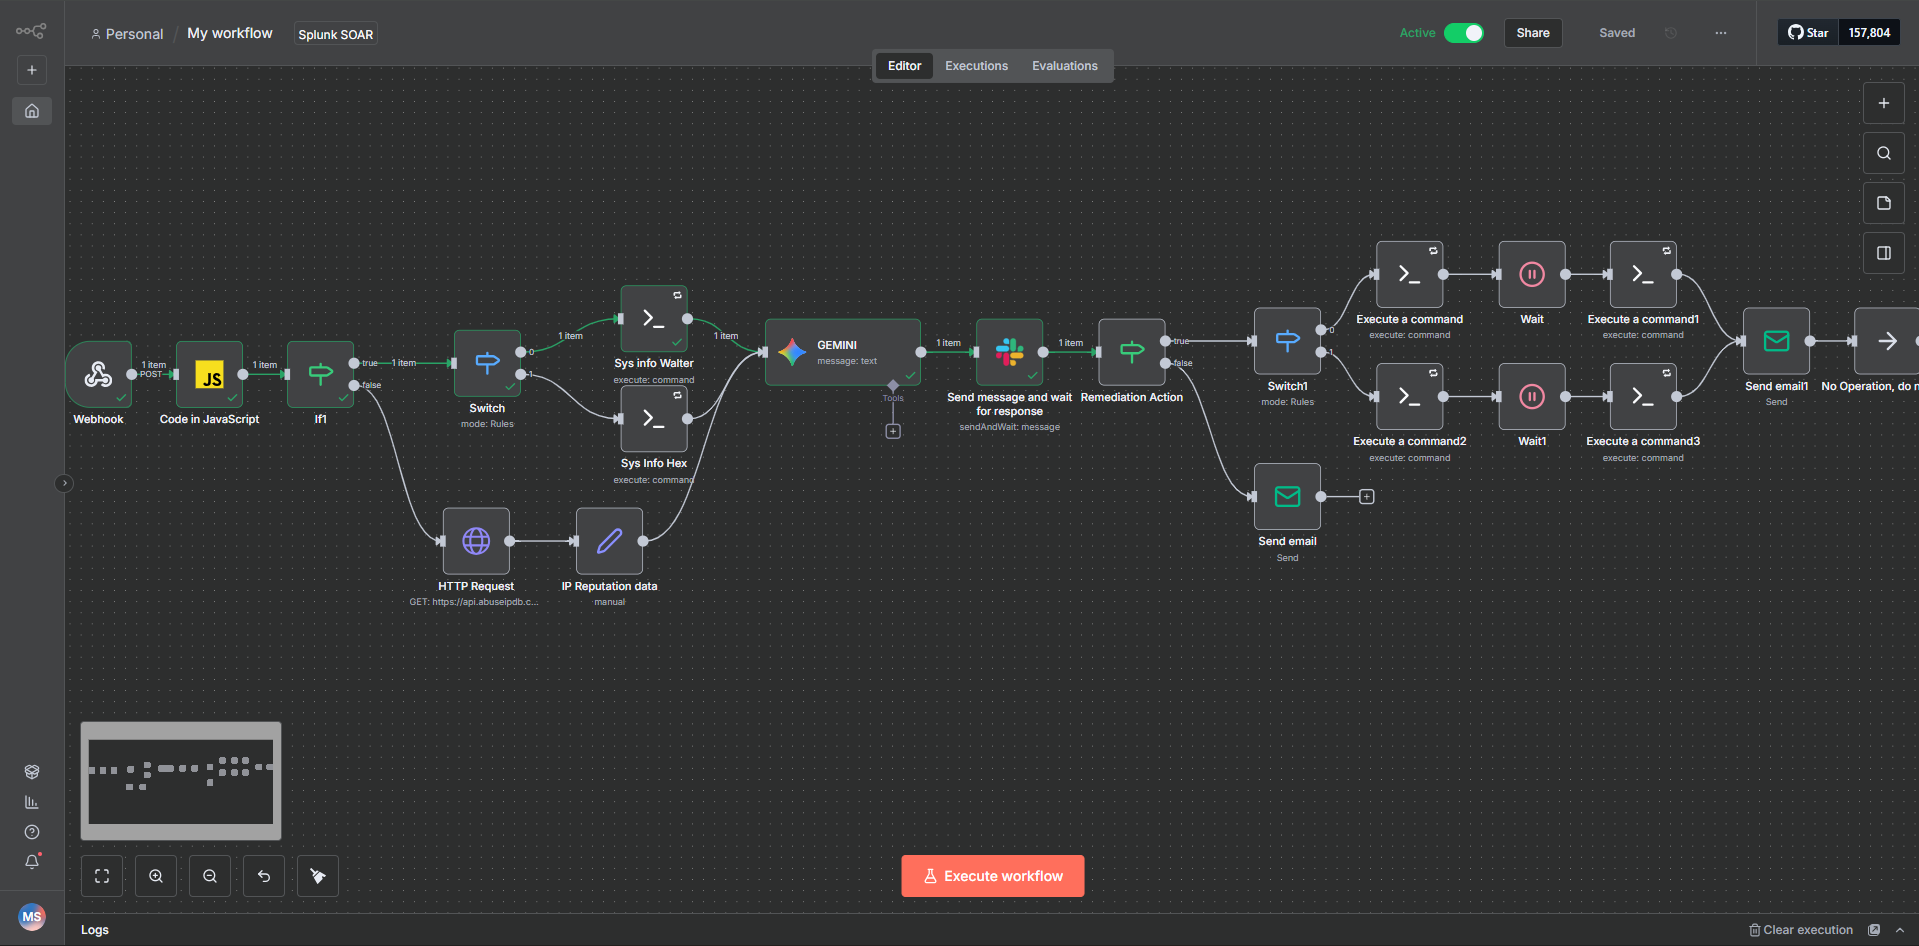
AI-Powered SOC Automation Lab
Engineered a fully automated SOAR workflow integrating Splunk for detection and n8n for orchestration to mitigate SSH brute-force attacks. Integrated Google Gemini AI to analyze live forensic data and implemented 'Human-in-the-Loop' active defense for one-click firewall remediation.
Experience
Where I've Worked
Software Co-Op
 Globus Medical
March 2026 - Present
Performed system security assessments and vulnerability analysis on enterprise endpoints by leveraging industry-standard tools such as Nessus Essentials and Nmap. Conducted network and host-based scans to identify open ports, misconfigurations, and potential security risks.
Executed compliance evaluations using SCAP Compliance Checker to assess systems against Security Technical Implementation Guides (STIG) benchmarks, ensuring adherence to security best practices and regulatory requirements.
Analyzed scan results to identify vulnerabilities, prioritize risks, and support remediation efforts to strengthen system security posture. Collaborated with team members to improve endpoint hardening, reduce attack surface, and maintain compliance with organizational security policies.
Technology Support Associate
 Heuristic Pharma Perceptions Private Limited
December 2024 — April 2025
Designed and implemented security measures to safeguard web applications, servers, and databases from potential vulnerabilities.
Applied industry best practices such as encryption for Personally Identifiable Information (PII), optimal password hashing algorithms, and enforced SSL for secure data transmission.
Mitigated security risks through input sanitization techniques on both client and server sides to prevent injection attacks.
Ensured compliance with security standards via comprehensive testing strategies including unit testing and advanced vulnerability assessments.
Created a structured security testing document to validate controls across multiple layers and ensure resilience against cyber threats.
Contributed to building a secure digital environment by integrating proactive measures that protect user data, maintain system integrity, and uphold security compliance.
Blog
Latest Articles
How to Set Up a VPN with Tailscale: Overcoming CGNAT Challenges
This writeup details how to set up a VPN using Tailscale to bypass Carrier-Grade NAT (CGNAT) restrictions, configure an Ubuntu exit node, and leverage Tailscale's peer-to-peer mesh network.
Read article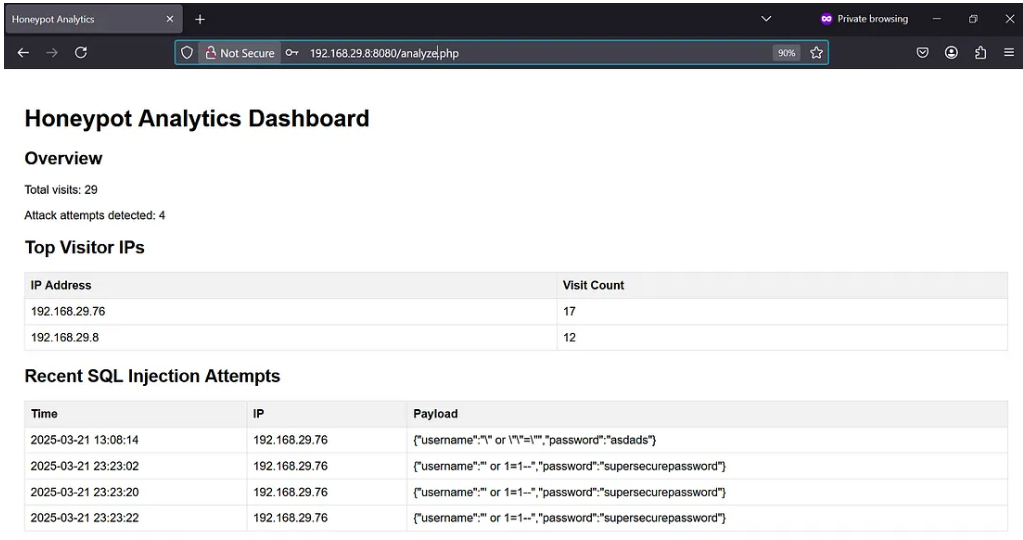
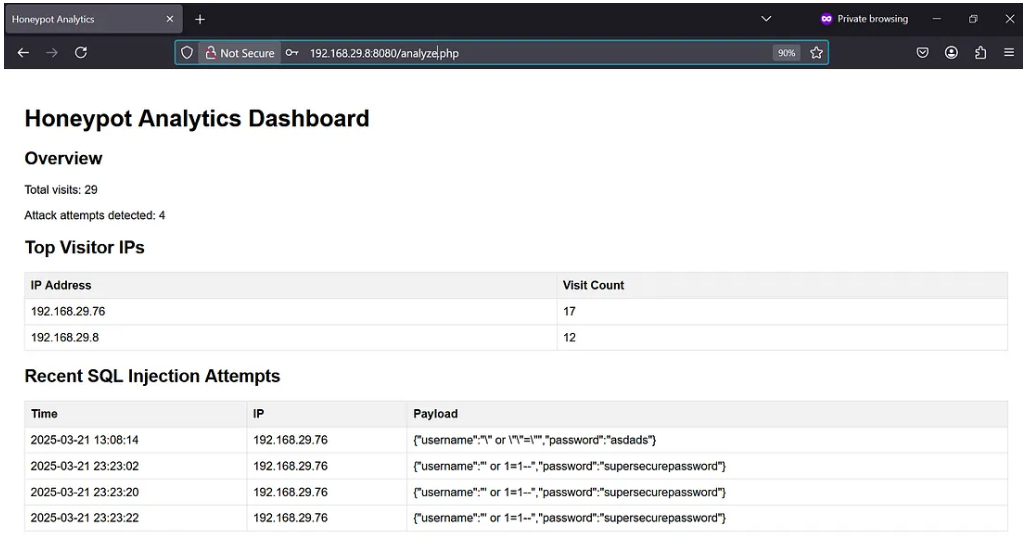
How to Set Up a Honeypot for Your Apache2 Server
In today's world, where bots, script kiddies, and sophisticated attackers roam the internet, I wanted to go a step further — not just protect my site, but also learn about the threats targeting it.
Read article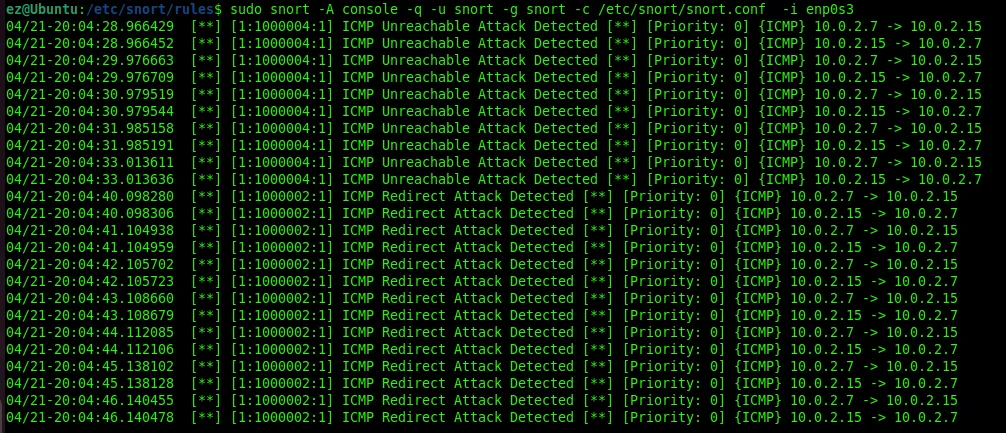
Detect ICMP Attack using Snort IDS
This project aims to install and configure the SNORT intrusion detection system on an Ubuntu Linux machine to demonstrate how an ICMP attack can be detected.
Read article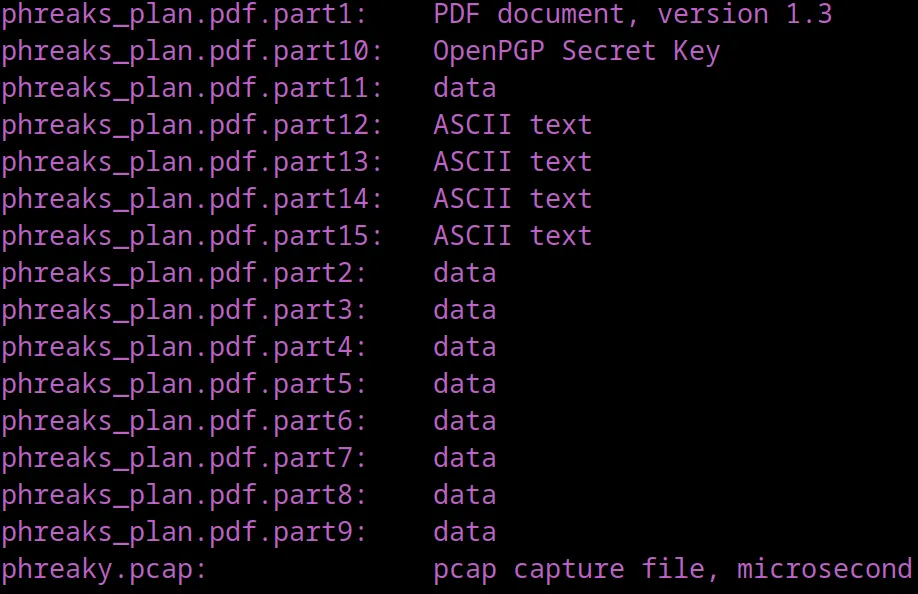
Phreaky [HTB CTF Try Out]
In the shadowed realm where the Phreaks hold sway, a mole lurks within, leading them astray. A network packet capture must reveal the trick.
Read article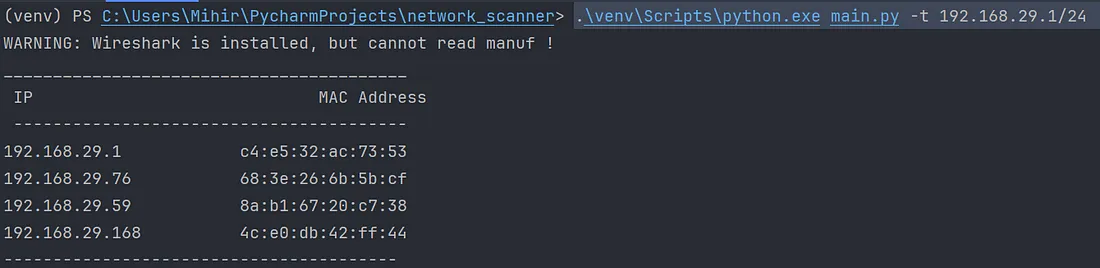
Building Network Scanner using Python with Scapy
In this tutorial, we will use Python to create a simple yet effective network scanner using ARP scanning over a specified IP range.
Read article
HTB RedTrails Forensics Challenge
This is a writeup for the RedTrails forensics challenge on HackTheBox, where we analyze a memory dump to uncover hidden artifacts using Volatility.
Read article
HTB m0rsarchive Write-up
This writeup covers the m0rsarchive challenge from HackTheBox, a forensics challenge involving the analysis of a Morse code audio file.
Read articleCredentials
Education & Certifications
B.Tech in Computer Science and Engineering
Navrachana University
2021 — 2025
B.Tech in Computer Science and Engineering with a focus on cybersecurity and network security.
CompTIA Security+
CompTIA
August 2025
Essential knowledge in network security, cryptography, identity management, and threat mitigation.
Google Cybersecurity Professional Certificate
Coursera
Dec 2023 — Nov 2024
8-course program covering foundations of cybersecurity, risk management, Linux, SQL, network security, incident detection, and Python automation.
SOC Analyst Job Role Path
HTB Academy
Oct 2024 — Present
Covers security monitoring, SIEM analysis, traffic inspection, and DFIR through hands-on labs and real-world scenarios.
Contact
Get In Touch
I'm currently looking for new opportunities in cybersecurity. Whether you have a question or just want to say hi, feel free to reach out.